Keynote Speakers
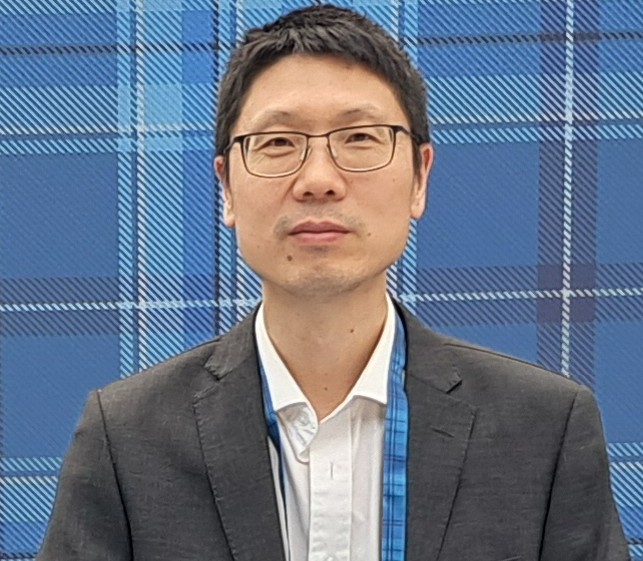
Dr. Qinghua Wang
Kristianstad University, Sweden
Qinghua Wang is an Associate Professor of Computer Science at Kristianstad University, Sweden, where he previously led the Research Environment of Computer Science (RECS) from 2019 to 2024. He received his B.Eng. degree from Harbin Engineering University, China, in 2002 and his Ph.D. degree from Mid Sweden University, Sweden, in 2010. From 2010 to 2013, he held postdoctoral research positions at the Norwegian University of Science and Technology and Aalto University. He was promoted to Docent at Kristianstad University in 2017. His research spans the Internet of Things, artificial intelligence, wireless systems and network security. His current work focuses on zero-trust and AI-driven security for 6G, including cross-layer authentication, physical-layer security, resilient AI and post-quantum migration. He has authored or co-authored more than 50 publications. Since 2025, he has served as Chair of the IEEE Sweden Section.
Title: Zero Trust for AI-Native 6G: From Cross-Layer Trust Evidence to Continuous Security Assurance
Abstract:
Sixth-generation networks are expected to support massive Internet of Things deployments, autonomous systems, edge intelligence and services spanning multiple administrative and technological domains. These characteristics challenge conventional security models based on fixed perimeters, implicit trust and one-time authentication. Moreover, the growing dependence of 6G on artificial intelligence introduces a dual challenge: AI can strengthen security decisions, but it also creates new attack surfaces and sources of uncertainty.
This keynote examines how zero-trust principles can be extended from enterprise networks to the dynamic, distributed and resource-constrained environment of 6G. It argues that identity credentials alone are insufficient for establishing trust in devices, users and network functions. Instead, security decisions should be continuously supported by cross-layer evidence, potentially including cryptographic credentials, physical-layer and radio-frequency characteristics, device and runtime attestation, behavioural observations, and confidence information from AI-based security functions.
A conceptual architecture is presented for collecting and evaluating such evidence and translating it into adaptive authentication, authorization and policy-enforcement decisions. Particular attention is given to the reliability of trust evidence: measurements may be noisy, context-dependent, manipulated or privacy-sensitive, while AI models may be affected by poisoning, evasion, concept drift and unreliable confidence estimates. The keynote also discusses the roles of local enforcement, network-wide orchestration, explainability, human oversight and post-quantum migration.
Drawing on research in wireless security, IoT authentication, device fingerprinting and resilient AI, the talk identifies open challenges and proposes a research agenda for making zero trust in 6G measurable, interoperable and resilient. The objective is not to assign permanent trust, but to enable defensible security decisions under continuously changing conditions.
ACDSA
International Conference on Artificial Intelligence,
Computer, Data Sciences and Applications
Contact
ECER EventsWorld Wide Commercial Building, No:72
Al Hilal, D Ring Road, Doha, Qatar
WhatsApp: +974 72021173
E-mail: info@acdsa.org
Social Media


